← All productsSecurity intelligence / On-premise
See more. Detect faster. Stay ahead.
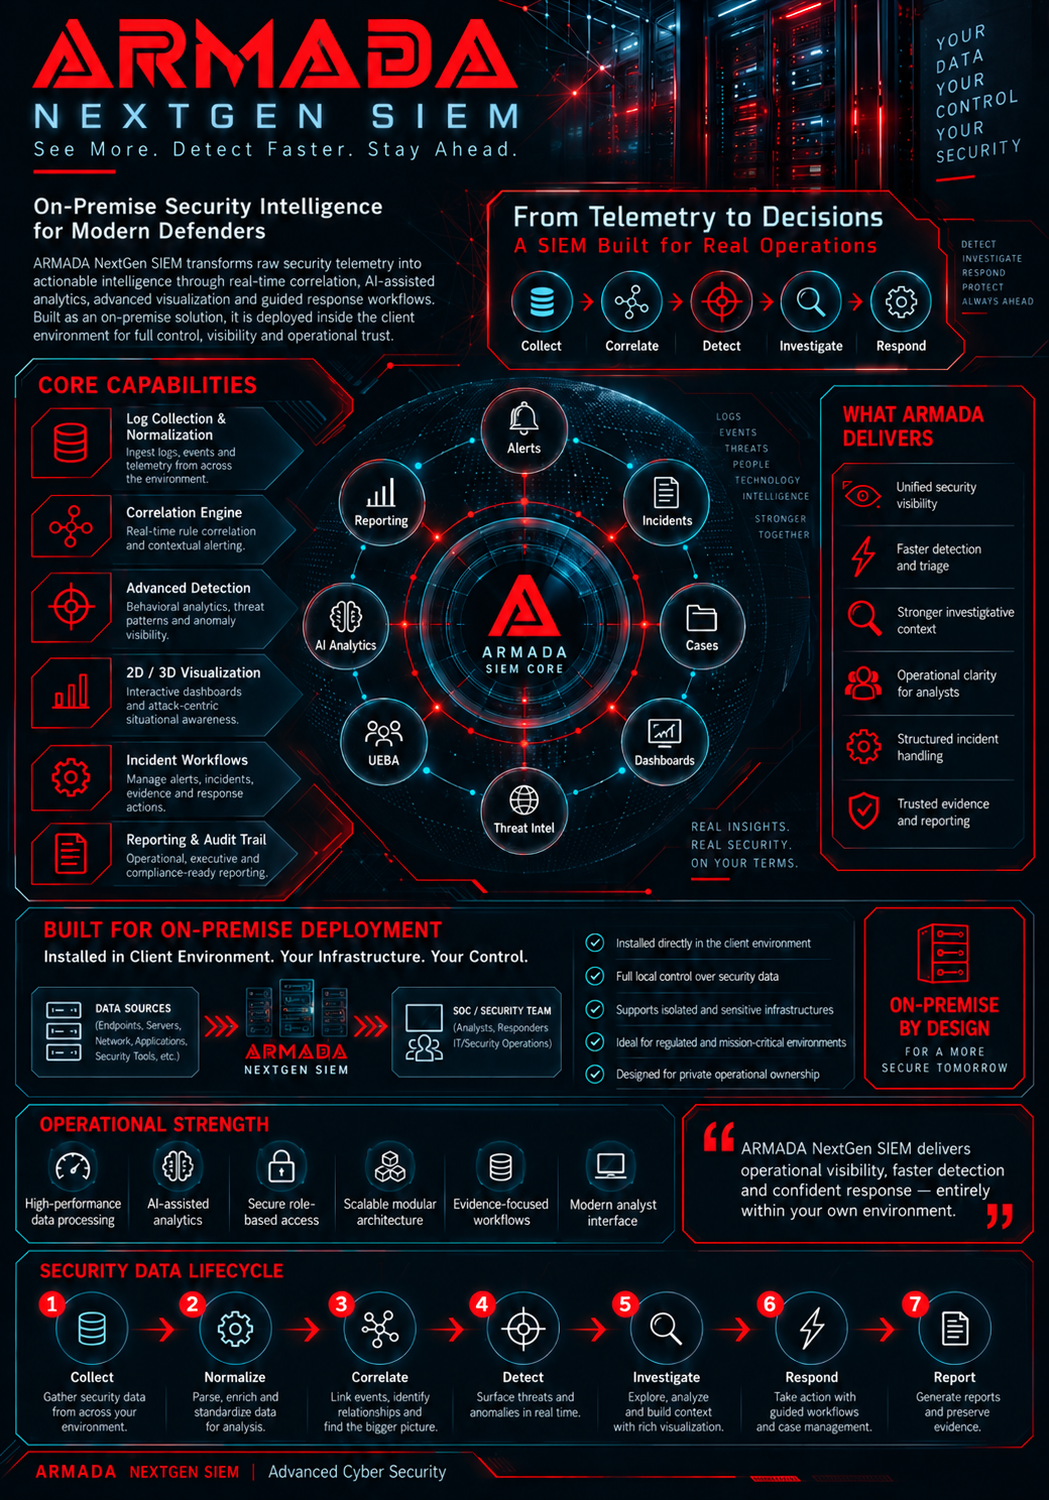
On-premise security intelligence for modern defenders. Transform raw security telemetry into actionable intelligence through real-time correlation, AI-assisted analytics, advanced visualisation and guided response workflows — within your own environment.
A SIEM built for real operations
From telemetry to decisions
- 01 Collect security telemetry
- 02 Correlate events and context
- 03 Detect threats and anomalies
- 04 Investigate the connections
- 05 Respond with guided workflows
Your data. Your control. Your security.
Inside ARMADA NextGen SIEM
See the connections behind the alerts
Explore event relationships, correlated alerts and supporting logs in a connected investigation view.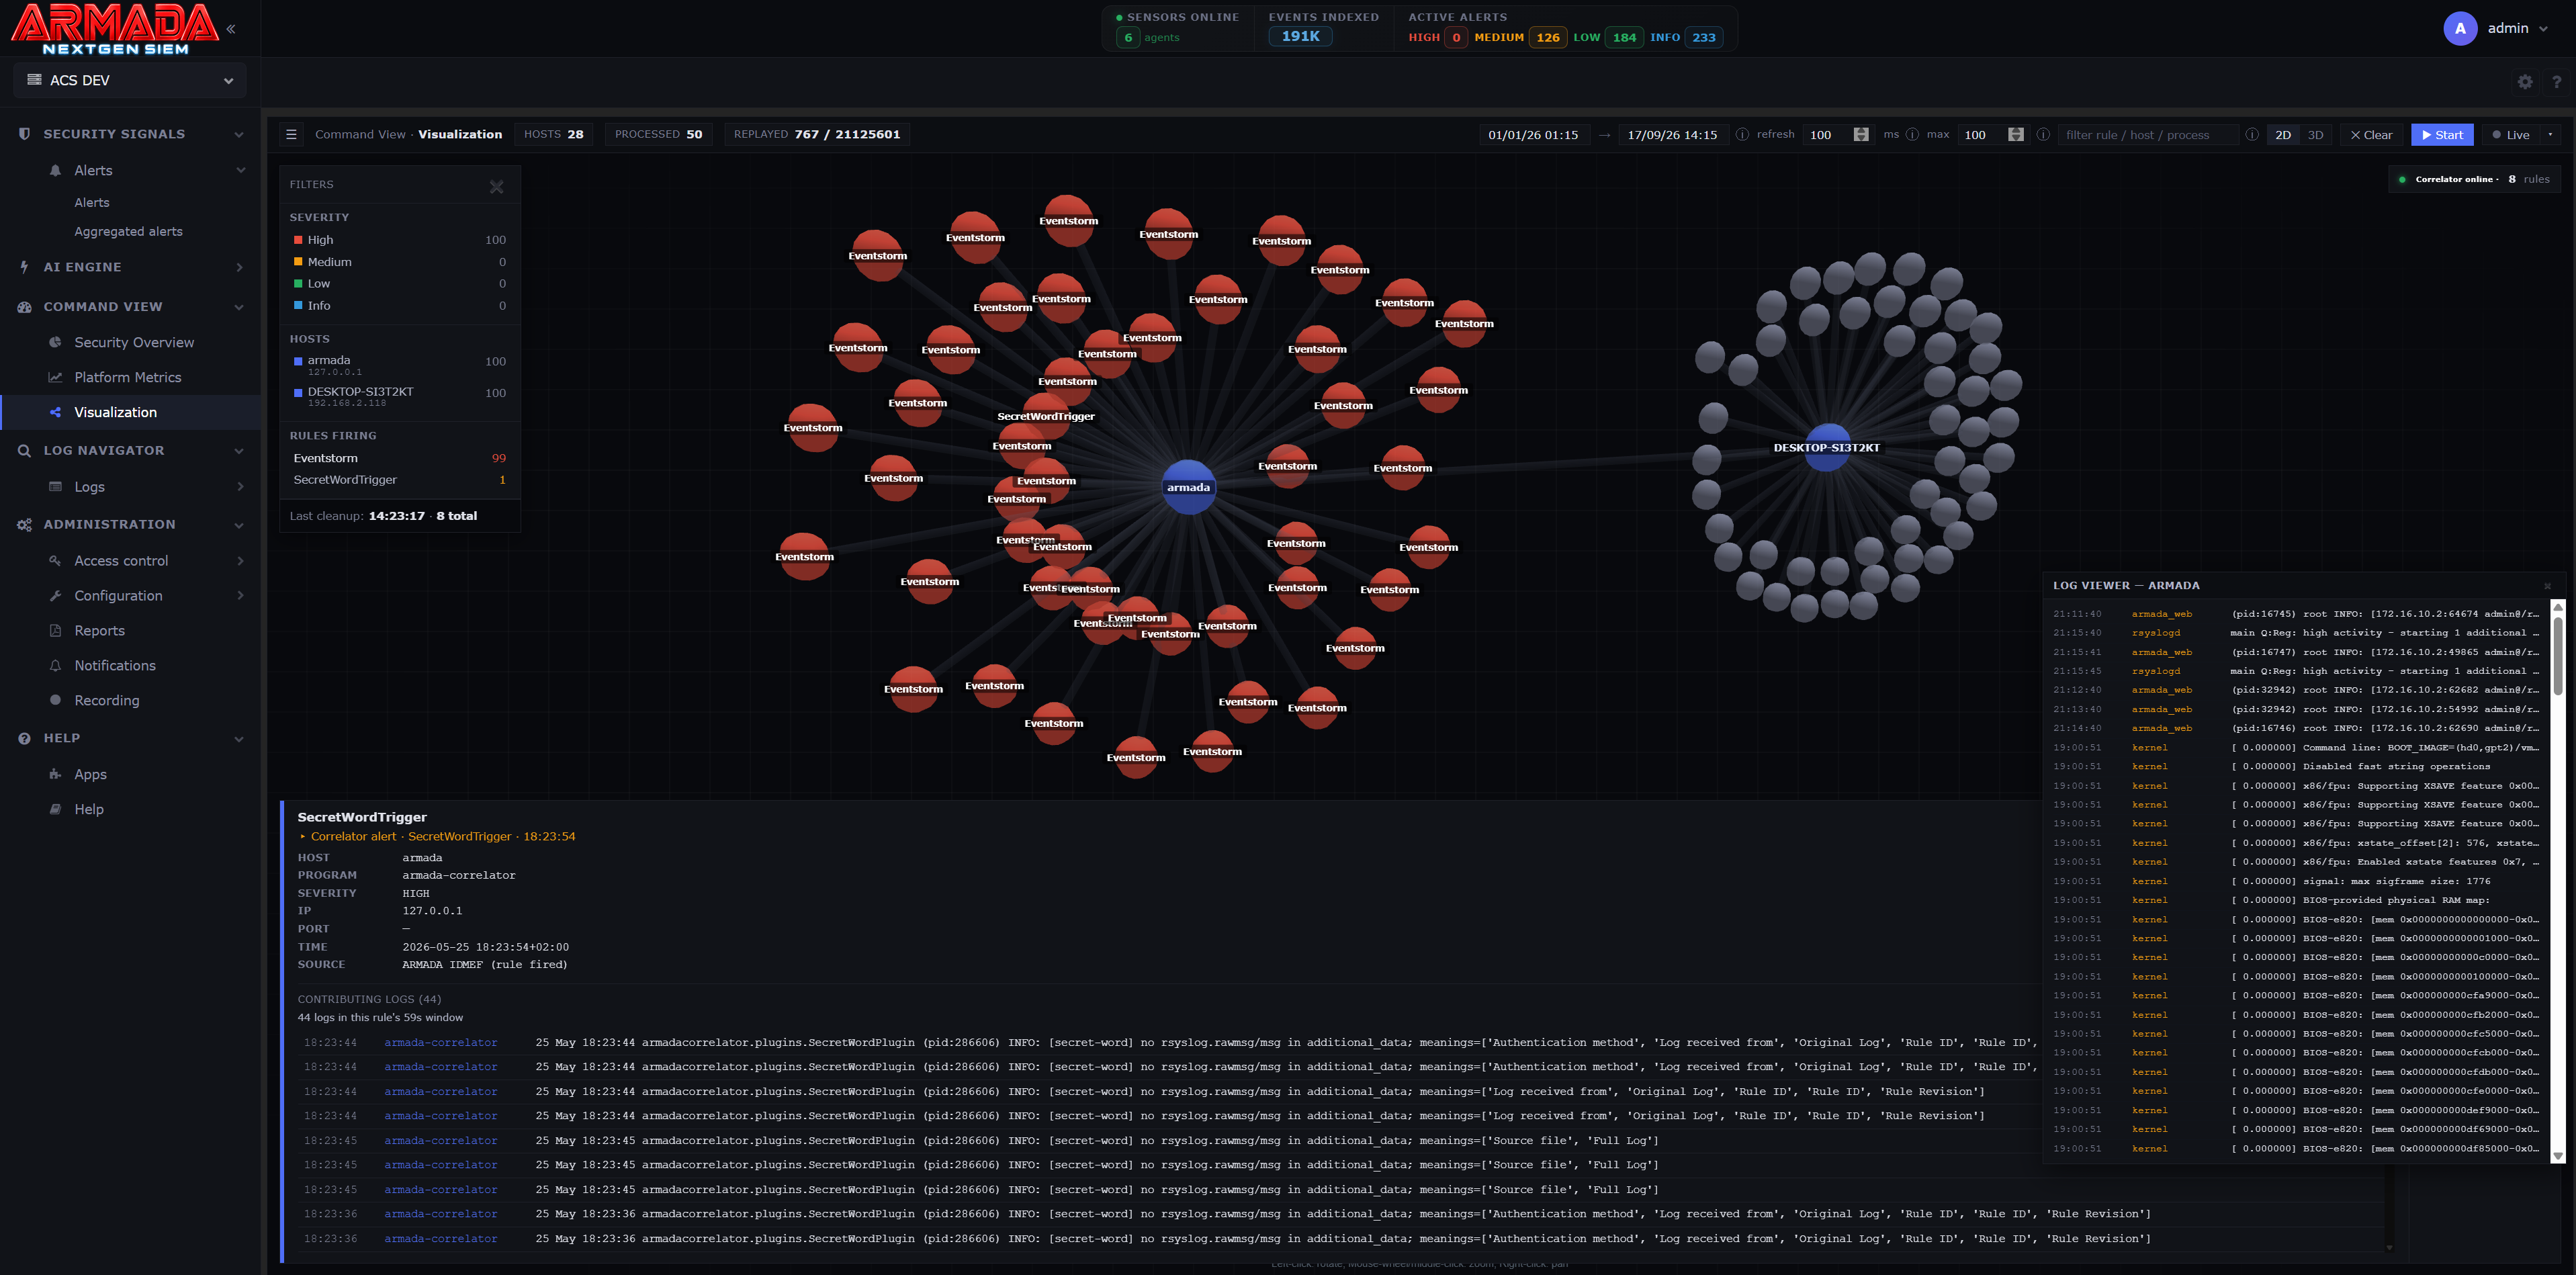
Core capabilities
Security data with operational meaning
Bring visibility, investigative context and incident handling into a connected security workflow.
01 / COLLECT
Log collection & normalisation
Ingest logs, events and telemetry from across your environment. Parse, enrich and standardise data for analysis.
02 / CONNECT
Correlation engine
Apply real-time rule correlation and contextual alerting to link events, identify relationships and find the bigger picture.
03 / DETECT
Advanced detection
Use behavioural analytics, threat patterns and anomaly visibility to support detection and triage, with AI-assisted analysis.
04 / VISUALISE
2D / 3D visualisation
Explore interactive dashboards and attack-centric views to understand relationships and build situational awareness.
05 / INVESTIGATE
Incident workflows
Manage alerts, incidents, cases and evidence. Connect investigation with guided response actions and structured handling.
06 / REPORT
Reporting & audit trail
Generate operational, executive and compliance-ready reporting while preserving evidence and the investigation trail.
On-premise by design
Your infrastructure Your control
Installed directly in the client environment, ARMADA NextGen SIEM keeps security data under local control. It supports isolated and sensitive infrastructures and is designed for private operational ownership.Data sources
Endpoints, servers, networks, applications and security toolsARMADA NextGen SIEM
Collection, correlation, detection and security intelligenceSOC / security team
Analysts, responders and IT/security operationsRole-based accessModular architectureEvidence-focused workflowsLocal data control
Security data lifecycle
From collection to a clear response
- 01
Collect
Gather security data from across your environment. - 02
Normalise
Parse, enrich and standardise data for analysis. - 03
Correlate
Link events and identify relationships. - 04
Detect
Surface threats and anomalies in real time. - 05
Investigate
Explore the evidence and build context. - 06
Respond
Act through guided workflows and case management. - 07
Report
Generate reports and preserve evidence.
Product overview
Explore ARMADA NextGen SIEM
See the core capabilities, operational model and on-premise deployment approach in the product one-pager.